Independent assessments that identify gaps across people, process, and technology — then turn findings into a clear, prioritized action plan your team can execute.
Many organizations discover weak points only after a break-in, policy failure, or near miss. Our consulting work gives leadership a factual picture of exposure — physical, procedural, and operational — so investment goes where it reduces risk fastest.
Recommendations stay practical. We align findings with your budget, staffing model, and the services you already use such as guarding or integrated technology.
Perimeters, lighting, locks, camera coverage, and patrol patterns reviewed against real site conditions.
Who can enter, when, and with what oversight — including visitor, vendor, and after-hours controls.
Post orders, escalation paths, key control, and incident reporting tested for clarity and consistency.
Emergency readiness, single points of failure, and recovery gaps that can stop operations cold.
We do not deliver a generic checklist. Each engagement follows a repeatable method tailored to your sites and industries.
Define locations, assets, threat concerns, compliance drivers, and the decisions leadership needs to make.
Walk facilities, interview stakeholders, review current posts and systems, and document observable vulnerabilities.
Rate likelihood and impact, group findings by theme, and separate quick wins from longer capital projects.
Present a clear report with prioritized recommendations, ownership suggestions, and optional service options.
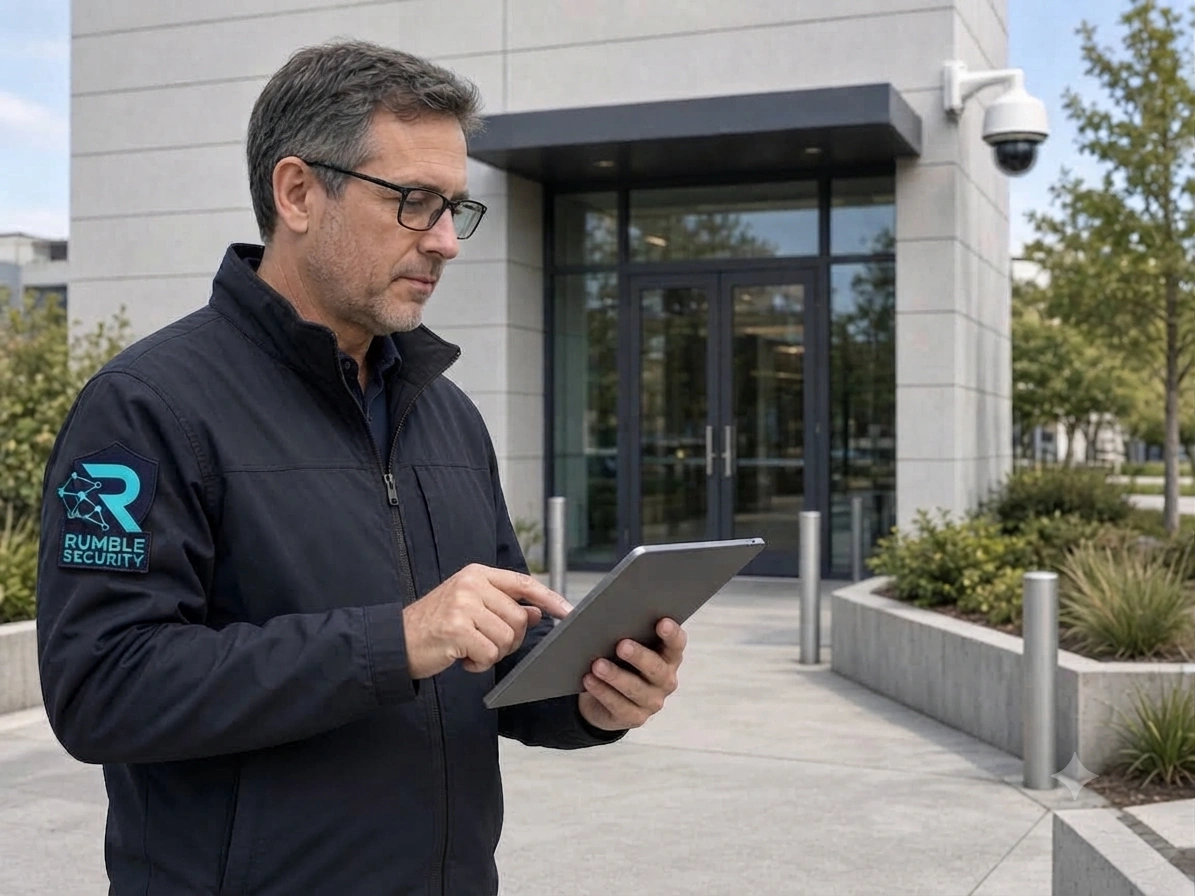
Assessments combine outdoor perimeter reviews with interior walkthroughs — blind spots, approach paths, lighting dead zones, unsecured doors, and camera angles that look good on paper but fail in practice.
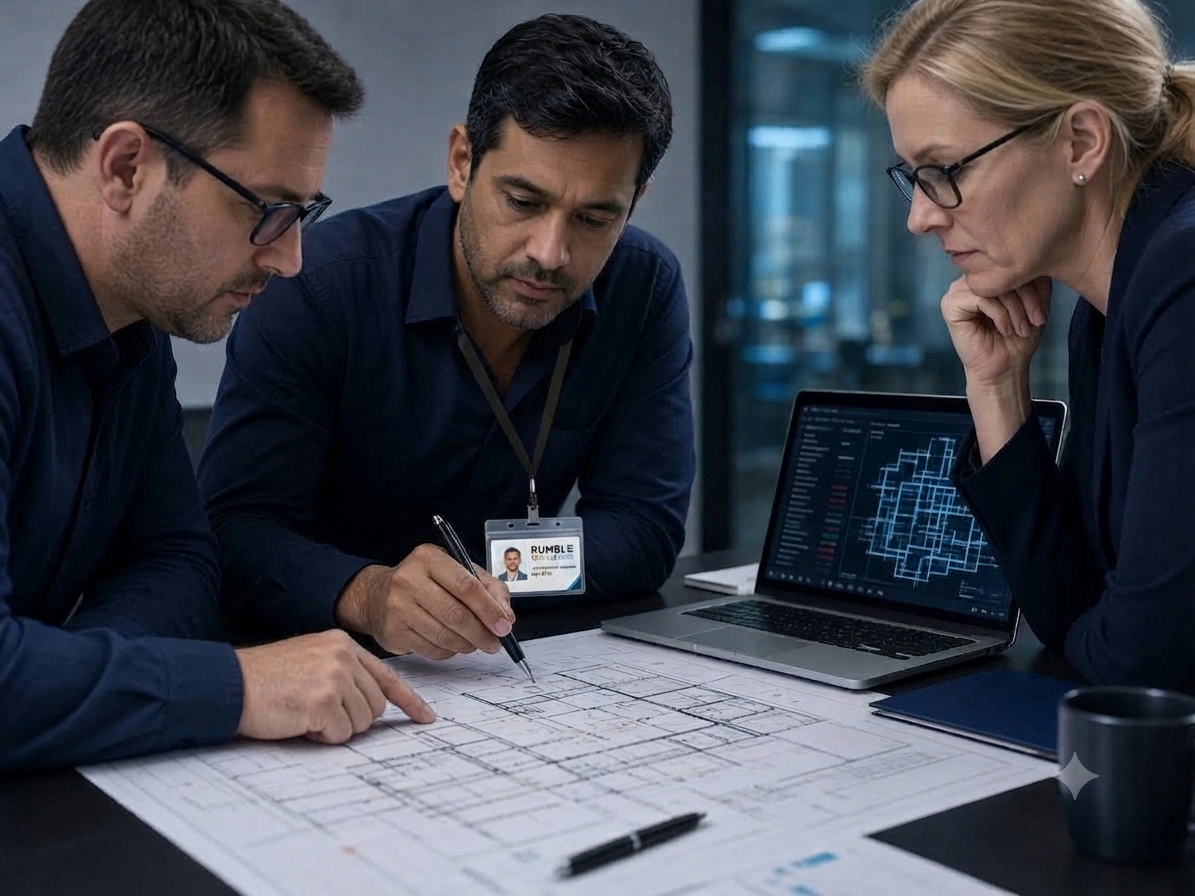
Every engagement ends with documentation you can share with executives, facilities, and security partners — not a vague summary.
We facilitate working sessions so facilities, HR, operations, and security stop debating symptoms and agree on the highest-value controls first.
That shared view makes budget conversations faster and reduces duplicate spend across vendors.
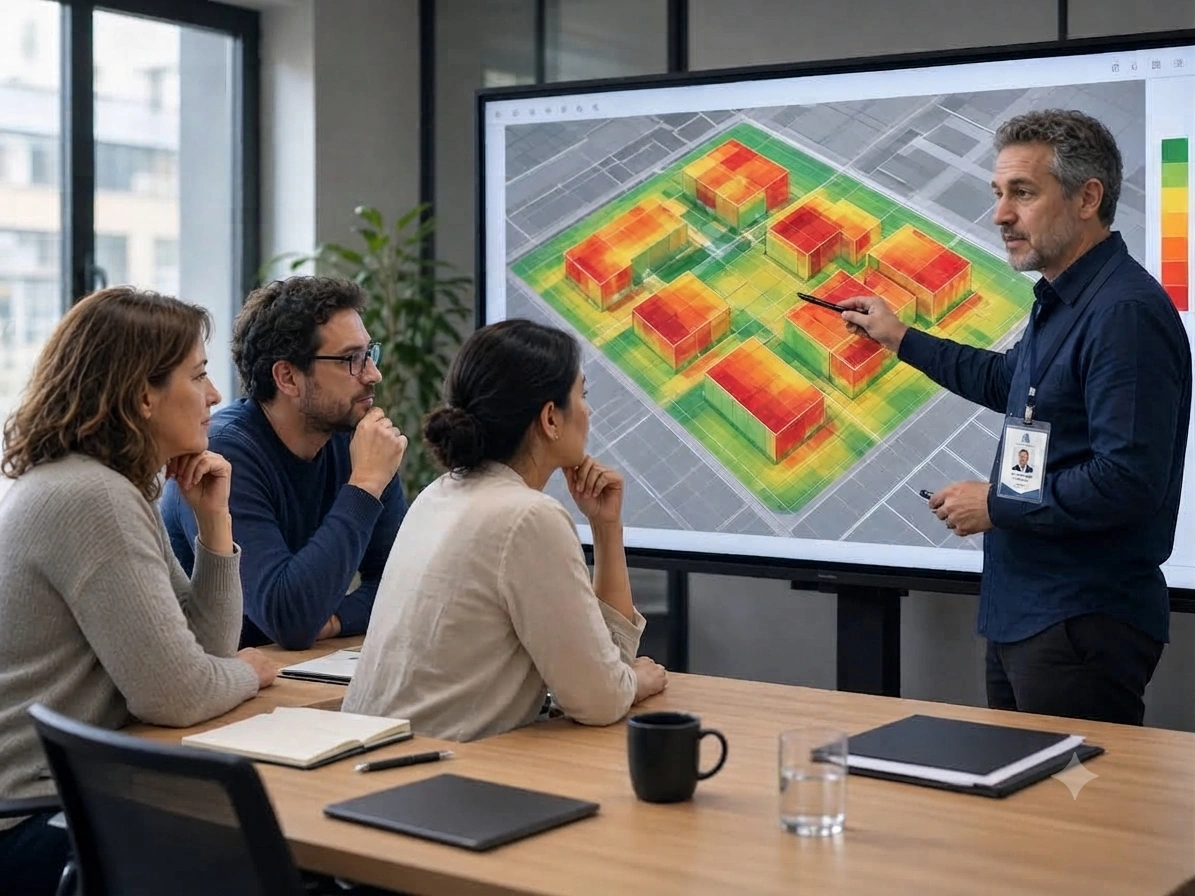
Standard scoring and reporting keep multi-location programs comparable, while still capturing the unique risks of each property, neighborhood, and operating model.
Most single-site reviews complete within days of the walkthrough, with a briefing shortly after analysis. Multi-site programs are scheduled in phases.
No. Findings come first. Where Rumble services help close a gap we will say so; where process or third-party changes are better, we document that clearly.
Yes. Post-incident reviews help reconstruct what failed and prevent repeat exposure while support teams stabilize the site.
Typically security leads, facilities, and decision-makers who control budget. We can also prepare a shorter board-ready summary.
Tell us about your sites and concerns. We will outline a scoped assessment and expected deliverables.